Quick Answer: Louis Rossmann withdrew his long-running recommendation of Privacy.com after it paused his account and asked him to send his ID and a face scan to Persona, a verification vendor that may keep biometric data for up to three years. For people who still want masked, controllable virtual cards, Halocard is the strongest replacement: it publishes what it collects and who keeps it, needs no linked bank account, and works in 120+ countries.
For years, Louis Rossmann, the repair technician and consumer-rights YouTuber with more than 2 million subscribers, told his audience to use Privacy.com for virtual cards. In a video published in late September 2026, he took that advice back and apologised for giving it.
Within days the Privacy Guides community had opened a thread proposing Privacy.com be dropped from its recommendations, Halocard's CEO, Ed, had recorded a reaction video walking through Rossmann's points one by one, and Privacy Guides had published its own response arguing the issue is bigger than any single provider.
This guide covers what Rossmann objected to, what the verification vendor at the centre of the story actually does, the pattern behind Privacy.com users' own complaints, where Rossmann's argument is strongest and where it needs context, how Ed responded, and which card service makes sense now if you are leaving Privacy.com.
Key Takeaways
- Louis Rossmann revoked his Privacy.com endorsement in late September 2026 after a paused account demanded biometric verification through Persona.
- The Persona consent screen asked permission to use his biometric data to improve Persona's own platform and to store it for up to three years.
- A February 2026 code exposure showed Persona's system could run up to 269 checks, which is why privacy-minded users distrust this vendor in particular.
- A Privacy.com customer's BBB complaint shows the company declining to delete ID and selfie images, citing federal recordkeeping rules the customer disputes.
- Privacy Guides argued the deeper problem is weak US data privacy law and has not dropped Privacy.com while its community debates the question.
- Halocard's CEO agreed with Rossmann's core complaint and has started a review of what Halocard's own verification vendor retains.
- Halocard fits people who want private payments with honest data disclosures, although no regulated virtual card can make you anonymous.
Timeline: How the Privacy.com and Persona Story Unfolded
Most coverage treats Rossmann's video as the start of this story. It was the moment it reached a mass audience, but the warning signs had been building for more than eighteen months.
| Date | Event |
|---|---|
| February 2025 | Privacy Guides forum members report Privacy.com asking some customers for a selfie and photo ID through Persona |
| July 8, 2025 | The Eighth Circuit strikes down the FTC's click-to-cancel rule days before enforcement |
| July 2025 | A Privacy Guides forum thread argues Privacy.com's name overstates its privacy, citing its data-sharing policy and bank statements |
| September 2025 | An App Store reviewer complains about selfie, ID and SSN requirements and an unanswered account deletion request |
| February 4, 2026 | Sumsub, the verification vendor Halocard uses, discloses a July 2024 intrusion into a support environment |
| February 2026 | Researchers find Persona frontend code on a public FedRAMP-authorised server describing 269 possible checks |
| February 20, 2026 | A Privacy.com customer files a BBB complaint after the company declines to delete their ID and selfie images |
| March 2026 | Persona tells Malwarebytes the exposed system was an isolated test environment with no personal data |
| September 24, 2026 | A Privacy Guides member proposes removing Privacy.com from the site's recommendations |
| Late September 2026 | Louis Rossmann publishes his video revoking his Privacy.com endorsement |
| September 26, 2026 | Halocard's founder posts on the Privacy Guides forum explaining US identity rules |
| September 29, 2026 | Halocard's CEO publishes a reaction video and commits to reviewing what Sumsub retains |
| September 30, 2026 | Privacy Guides publishes its own video arguing the root problem is weak privacy law |
| September 30, 2026 | A new one-star App Store review says Persona ID verification ruined the app |
Why Louis Rossmann Recommended Privacy.com in the First Place
Rossmann never pitched Privacy.com as a privacy product in the abstract. He used it as a weapon against two billing tactics he runs into constantly, and both explain why his reversal stung his audience.
The Cancellation Workaround
His first complaint is the subscription that is easy to start and almost impossible to stop. He describes free trials priced at $29.99 a month where finding the cancel button is, in his words, harder than repairing a motherboard without a schematic.
His fix was simple: when a vendor makes cancellation miserable, he swaps a fresh virtual card onto the account, closes that card, and leaves the company with nothing to charge. As he puts it, that becomes the cancellation.
The tactic is more useful than it sounds, because the federal safety net people expected never arrived. The FTC's click-to-cancel rule, which would have forced businesses to make cancelling as simple as signing up, was struck down by the Eighth Circuit in July 2025, days before enforcement was due to begin.
Meanwhile, Security.org's 2026 fraud survey found that 22% of fraud victims had faced recurring unauthorised charges from the same merchant, up from 12% in 2024, a trend the researchers tie partly to dark-pattern subscription billing. A card you control is the one lever that works regardless of what the merchant allows.
Spending Limits as an Early Warning
His second use case is the quiet price rise. Rossmann describes paying $100 a month for a service, then receiving a no-reply email that looked like spam announcing the bill would become $130, with no opt-in required. By capping that card at $100 per transaction or per month, the higher charge simply declined. He calls this creating a pain point: the failed payment is what alerts him that the terms changed.
This is also what independent researchers recommend. The same Security.org study found 51% of cardholders still put recurring autopay and everyday purchases on one card, which it describes as a single point of failure, and advises keeping daily spending and subscriptions on separate cards. Rossmann's setup did exactly that, one capped card per vendor.
Our guide to managing SaaS subscriptions with virtual cards shows the same method applied to software bills, and how to use a virtual card covers the basics if you are new to the idea.
What Changed: The Persona Verification Prompt
The break came from a single login. Rossmann went to swap a card in on a vendor he wanted to escape and found his Privacy.com account frozen behind an identity check.
What the Prompt Asked For
The screen told him his account was paused and that Privacy.com needed more information to confirm who he was. Clicking through meant agreeing that Persona, Privacy.com's verification vendor, and its own service providers could process his biometric information for three purposes: verifying his identity, detecting fraud, and improving Persona's platform under Persona's privacy policy.
The first two purposes are standard. The third is what set him off. Agreeing to let a third party use your face data to improve its own product is a different request from proving you are who you say you are, and Rossmann's point is that it runs directly against the reason anyone signs up for a service with "privacy" in its name.
The Three-Year Retention Window
The same notice said his biometric information would be stored for no more than three years. Rossmann read that as a ceiling with no visibility underneath it: three years if he is lucky, and no way of checking if it is longer. He was blunt that he does not want his data kept that long or used to train anyone's system.
It is worth knowing this was not brand new. Members of the Privacy Guides forum had reported Privacy.com routing some customers to Persona for a selfie and ID check since at least February 2025, and Ed noted in that same forum thread that Persona appeared to be a fallback for accounts where the original verification method was no longer enough. What changed is that it happened to someone with a very large audience who had vouched for the service.
Why Rossmann Held Himself Accountable
Rossmann stressed that Privacy.com never paid him. He says his channel has gone almost 15 years without sponsors, and he received no special treatment for recommending the service. His reasoning is that recommending something to millions of people creates the same duty as being paid to promote it: if it changes, you tell them.
That standard, applied to himself, is why the video carried weight. He was not settling a score; he was correcting advice he had given.
He was also clear about the limits of what he knew. He said he did not know the company's full history or whether management had changed, only that this was not the Privacy.com he had been recommending, and that he would no longer use or endorse it.
Why Persona Specifically Worries Privacy Users
Rossmann called Persona one of the worst identity verification services around. That is his opinion, but it rests on a real incident that circulated widely in 2026, and on a funding link he raised directly.
The February 2026 Code Exposure
In February 2026, security researchers looking into Discord's age checks found frontend code belonging to Persona sitting on a publicly reachable server authorised under FedRAMP, the US government's cloud security programme.
According to Malwarebytes' report on the exposure, the roughly 2,456 files described up to 269 distinct verification checks, facial matching against watchlists and politically exposed persons, and screening for adverse media across 14 categories including terrorism and espionage. The data types listed included IP addresses, browser and device fingerprints, government ID numbers, phone numbers, names and faces, with retention of up to three years.
Rossmann referenced these findings in his video, including checks tied to US and Canadian financial-intelligence systems. Discord announced afterwards that it would stop using Persona for age verification.
What Persona Said in Response
Fairness requires Persona's side. In an update Malwarebytes added in March 2026, Persona said the exposed environment was a test system isolated from production, that no personal data was exposed, that no customer uses all 269 checks, that it does not work with any federal agency, and that its customers control how and when data is deleted.
That last point cuts both ways. If the customer controls deletion, then the retention period Rossmann saw is partly a choice his card provider made, which is exactly why the question belongs with the card company as much as the vendor. The BBB complaint covered later in this article shows what happened when one customer put that question to Privacy.com directly.
The Founders Fund Connection
Rossmann described Persona as funded by Peter Thiel. The accurate version is that Persona has raised money from Founders Fund, the venture firm Thiel co-founded, and was valued at $2 billion after a $200 million round in May 2025.
That link has drawn scrutiny because of Thiel's role in founding Palantir, although Persona's CEO has denied any operational relationship with Palantir or US government agencies. How much weight to give that funding history is a judgement call, but it is part of why the prompt landed so badly with Rossmann's audience.
What Privacy.com Users Say About the Virtual Cards
Rossmann is one voice. To see whether his experience is isolated, we went through five places where Privacy.com customers leave feedback and focused on complaints about the virtual cards themselves rather than general gripes.
Strip out the one-off frustrations and three structural issues remain. Privacy.com's cards are only as reliable as the account behind them, and that account can be paused for verification, funding changes or chargebacks. Its funding model depends on a live link to your bank, which brings Plaid into the picture and can cause declines when the connection breaks.
And its biggest privacy feature against your own bank sits behind a paywall. None of this makes Privacy.com a bad product, and plenty of users are happy with it. It does explain why Rossmann's experience resonated as widely as it did.
Our Privacy.com review sets out what reviewers report in more detail.
The Retention Question Nobody Else Is Covering
Most reactions to Rossmann's video argue about Persona's three-year window. A BBB complaint from February 2026 shows what actually happens when a customer asks Privacy.com to delete the images afterwards, and it is the most specific evidence available on how long your ID and face may stay on file.
What the Customer Asked For
The customer had already passed Persona verification. They then asked Privacy.com to delete their driver's licence and selfie images under the California Consumer Privacy Act.
According to the complaint, Privacy.com first pointed to Persona's privacy policy, then, after the customer noted that Persona acts as a processor on Privacy.com's instructions, cited federal anti-money-laundering rules as the reason the images had to be kept.
What Each Side Argued
The customer's position was that the Customer Identification Program rule at 31 CFR 1020.220 requires keeping identifying information and a description of the documents used, not the raw image files, and that keeping the photos added breach risk for no legal reason.
Privacy.com's March 2026 response argued that the rule's recordkeeping requirement covers all information obtained during verification, including the documents, and that data collected under the Gramm-Leach-Bliley Act is exempt from CCPA deletion rights. The customer rejected that answer and said they would escalate to federal and California regulators.
Why This Is Useful to You
We are not lawyers and will not settle the legal question here. What the exchange does establish is practical: if you verified with Privacy.com through Persona, you should expect your ID and selfie images to be retained, and a California privacy request may not change that.
The rule itself requires identifying records to be kept for five years after an account closes, so retention is a real factor in choosing any regulated provider, not just this one.
Halocard's stated approach is different in one specific way. Its Your Privacy page says verification data is permanently removed from Halocard's own servers once checks complete, while Sumsub and Visa keep what regulations require. That does not mean no copy exists anywhere, and Halocard says so. It does mean the card company itself is not holding your documents.
Is Rossmann Right? A Fair Reading
On the point he actually made, yes. On the wider conclusion some viewers drew, that identity checks are a sign a card service has gone bad, the picture is more complicated.
Where His Argument Holds
Rossmann objected to three specific things: biometric data used to improve a third party's product, a retention window measured in years, and a change that arrived as a locked account rather than an explanation. Each of those is a fair objection. None of them is required to issue a card, and a privacy-focused brand that accepts them without telling customers has a trust problem regardless of what the law demands.
Where It Needs Context
The identity check itself is not optional for anyone. Every US bank, and every company issuing cards on a bank's behalf, must run a Customer Identification Program under 31 CFR 1020.220, collecting at least a name, date of birth, address and an identification number, and verifying them by documentary or non-documentary means. A virtual card service with no identity check is either unregulated or about to be shut down.
The selfie step is different. The law does not strictly require a liveness scan; it is a fraud control. The reason providers lean on it is that faked documents have become cheap. Entrust's 2025 Identity Fraud Report recorded a deepfake attempt every five minutes in 2024, and found digital document forgeries rose 244% year over year, overtaking physical counterfeits for the first time.
A Problem Bigger Than One Company
Even privacy advocates who agree with Rossmann do not think the answer is simply abandoning one provider. Privacy Guides, which had recommended Privacy.com for years, answered with its own video on September 30, 2026. Its presenter, Nate Bartram, said he agreed with much of Rossmann's video, but argued that being asked for your identity to satisfy KYC law does not, on its own, make a service non-private, that Privacy.com probably could and should have chosen a different verification vendor, and that the lasting fix is comprehensive US data privacy law limiting what verification firms may use to confirm identity, how long they may keep it, and whether they may sell it. Privacy Guides has not removed Privacy.com while its community debates the question, and Halocard is not among the alternatives its video suggested.
The honest takeaway is that Rossmann exposed a category problem with one company's name on it. Every regulated card issuer hands your identity to a verification vendor. What separates providers is whether they tell you who that vendor is, what it keeps, for how long, and whether they push back on anything beyond what the law needs. Our explainer on whether virtual credit cards are safe covers the rest of that checklist.
How Halocard's CEO Responded
Ed, Halocard's founder and CEO, published a reaction to Rossmann's video a few days after it went up. He runs a direct competitor, and he said so on the Privacy Guides forum before sharing it, so weigh his view accordingly. What stands out is how much of Rossmann's argument he accepted.
Agreeing on the Problem
Ed opened by saying he agreed completely with Rossmann's frustration over hard-to-cancel subscriptions, adding that it is one of the main reasons Halocard customers use the product at all. He singled out the trick of swapping a virtual card onto an account just before renewal and then killing it, said he liked it, and joked that he might start using it himself.
The Legal Floor Under Every Card Issuer
He then explained the rules every issuer works within. US identity requirements for financial products date to 2001, when the Patriot Act set out how banks and their partners must know their customers to limit money laundering and terrorist financing. There are two routes.
- The non-documentary route checks your SSN against government and credit-bureau data and often confirms a linked bank account through a service such as Plaid.
- The documentary route scans a passport, driver's licence or national ID.
Ed was careful to label the next part as speculation rather than fact: Rossmann probably signed up years ago through the non-documentary route, and something about either his account or Privacy.com's policy later triggered a documentary check through an outside vendor.
The BBB response describing a periodic details update for all customers fits that explanation, although neither Ed nor Privacy.com has said so about Rossmann's account specifically.
Why Liveness Checks Exist
On the biometric step, Ed described what actually happens: after you scan your document, you take a selfie and slowly turn your head while software builds facial markers and confirms the live person matches the photo on the ID. Without that, anyone holding a picture of a stolen ID could pass verification as someone else.
He also made an admission most companies would avoid. Card issuers can only choose from a handful of verification providers, and in his words none of them are spectacularly great. All of them gather large amounts of data because the threat they face has changed: with consumer AI tools, anyone with a laptop can now produce a convincing deepfake, and the volume of fake applications has climbed sharply over the last two to three years.
What Halocard Is Changing With Its Own Vendor
The most concrete part of the response was about Halocard itself. Ed said Rossmann's video gave the company pause and that Halocard has gone back to its verification provider, Sumsub, with three requests:
- A full breakdown of every piece of data Sumsub collects from Halocard customers during onboarding
- An explanation of which signals actually decide whether a check passes or fails
- A mechanism to flag any residual data so it is either deleted straight away or excluded from training and unrelated uses
He described collecting enough data to stop fraudulent applicants as justified, calling it Halocard's legal and fiduciary duty, while questioning how much of what vendors gather serves that purpose and how much serves the vendor.
He said Halocard hopes to announce process changes in the near term. To be precise about status, those changes had not been published at the time of writing, so treat this as a stated commitment rather than a finished policy.
In practical terms, the reaction did three things Rossmann asked of companies generally. It named the vendor, explained what the data is for, and admitted where the industry falls short. Halocard's existing approach is set out on its Your Privacy page, and the reasoning behind it on Our Story.
Why Halocard Is the Best Privacy.com Alternative Right Now
If you accept that some identity check is unavoidable, the best replacement is the provider that is most open about that check, gives you the same controls Rossmann relied on, and avoids the structural problems Privacy.com's own users keep reporting. On those counts, Halocard is the strongest fit for most people leaving Privacy.com.
Its Data Practices Are in Writing
Halocard's privacy page states exactly what it verifies: your name, address, date of birth and a government ID, plus an SSN if you live in the US. It says that data is then permanently removed from Halocard's own servers, names Sumsub as the verification provider, and admits that Sumsub and Visa keep records for as long as regulations require.
It also says Halocard never sells or correlates customer data and that closing your account wipes what Halocard holds. Few card providers name their verification vendor at all, let alone the limits of what they can delete. The full detail sits in the Halocard privacy policy, and the technical side is covered on the Halocard security page.
Who Sees What With Each Service
The table below sets out who learns what about a single online purchase on each service. It is the comparison most coverage of this story leaves out.
| Who | Privacy.com | Halocard |
|---|---|---|
| The merchant | A virtual card number and whatever name and address you enter | A virtual card number and the billing address set on that card |
| Your bank | Each charge, with the merchant name visible unless paid Private Spend Mode is on | Only top-ups to your Halocard balance, and nothing at all if you fund with stablecoins |
| A bank-linking service | Plaid, when used to connect your account | None required |
| The card provider | Every transaction, tied to your verified identity | Every transaction, tied to your verified identity |
| The verification vendor | Persona, with ID and selfie images retained per the provider's policy | Sumsub, retaining records for the regulatory period |
| The card network | Every transaction | Every transaction (Visa) |
Neither column is anonymous. The difference is how many extra parties see your spending, and whether your own bank gets a merchant-by-merchant view by default.
What Halocard Does Not Do
A recommendation is only useful if the limits are clear, so here they are without softening.
- It still verifies your identity. Halocard uses Sumsub, and onboarding can include a selfie or liveness check. If any biometric step is unacceptable to you, Halocard will not solve that.
- Its vendor has had its own incident. In February 2026, Sumsub disclosed that an attacker reached a support environment in July 2024, exposing mainly names plus some emails and phone numbers for a limited set of accounts. Sumsub says biometric data and ID images were not accessed.
- It is not anonymous. Visa and the issuing partner see your transactions, as with any regulated card.
- It costs money. Plans start at $12 a month, while Privacy.com has a free tier. Referrals can offset Halocard's fee, but there is no permanent free plan otherwise.
One more limit, raised by Privacy Guides, deserves a straight answer. Any standalone virtual card service, Halocard included, is one more company holding your identity. If your own bank or card issuer already offers virtual numbers with the controls you need, using those avoids adding a party. Halocard earns its place when your bank offers nothing comparable, when you want a separate billing address and hard limits on every card, or when you live outside the US and the bank-native options are not available to you.
If you want a broader view, our best Privacy.com alternatives roundup covers other options, including ones with no subscription fee. Head-to-head comparisons are also available for Privacy.com vs MySudo vs Halocard, Privacy.com vs Revolut vs Halocard, Privacy.com vs Klutch vs Halocard and Privacy.com vs IronVest vs Halocard. See Halocard vs Privacy.com side by side.
Questions to Ask Any Virtual Card Provider About Verification
Rossmann's experience shows that the time to ask about verification is before you hand over your face, not after an account is paused. These are the questions worth putting to any provider, Halocard included, and the answers you should be satisfied with.
- Which company runs your identity checks? A provider that will not name its vendor is asking you to trust a party you cannot research.
- Is a selfie or liveness check always required, or only in some cases? Liveness is a fraud control, not a legal requirement, so ask when it is triggered.
- Can the vendor use my biometric data to train or improve its own products? This was the clause that ended Rossmann's endorsement. You want a clear no.
- How long are my ID images and selfie kept, and by whom? Ask separately about the card company and the vendor, since their answers may differ.
- What happens if I ask you to delete them? Ask for the specific legal basis if the answer is no, and whether it covers the images or only a description of them.
- What can trigger a paused account, and how do I get it reviewed? BBB complaints show pauses after funding changes, chargebacks and periodic re-verification.
- Can my bank see each merchant I pay? On some services this depends on your plan.
- Do you need a live connection to my bank account? A balance-based model avoids the stale-link declines users describe.
How to Move Off Privacy.com Without Missing a Charge
Leaving a virtual card service is where people get caught out, usually by a renewal that hits a dead card or a refund sent to one that no longer exists.
- List every merchant before you change anything. Export or screenshot the merchant list on each Privacy.com card, and note which bills run annually.
- Give each subscription its own card and set the cap just above the bill. A price rise then fails instead of slipping through, which is the exact pain point Rossmann was relying on.
- Set the billing address before the first charge. Some platforms check the address against the card on the first payment, and changing it afterwards can trigger a decline.
- Avoid chargebacks on the old account during the switch. If a Privacy.com charge needs disputing, raise it with Privacy.com first, and wait until it is settled before closing anything.
- Keep the old cards open for 30 days, then close the account and ask for deletion. Refunds go back to the card that made the purchase. When you do close, request deletion of your data in writing, and ask which records, if any, remain with Persona and for how long.
Frequently Asked Questions
Why Did Louis Rossmann Stop Recommending Privacy.com?
His account was paused and he was asked to verify through Persona under terms that allowed his biometric data to be used to improve Persona's platform and kept for up to three years. He said that was not the service he had been recommending and that he would no longer use or endorse it.
Is Privacy.com Still Safe to Use?
It remains a legitimate, regulated US service with a strong Trustpilot and App Store record and an A+ BBB rating, and Privacy Guides has not removed it from its recommendations, though its community is still debating the question. Whether it suits you depends on whether you are comfortable with Persona handling your verification and with your ID images being retained. Read the consent screen before you agree.
What Is Persona, and Why Is It Controversial?
Persona is a San Francisco identity verification company used for KYC and age checks by many large platforms. It drew criticism after researchers found its code exposed on a government-authorised server in February 2026, describing up to 269 checks. Persona says the system was an isolated test environment and no personal data leaked.
Will Privacy.com Delete My ID and Selfie If I Ask?
Based on a February 2026 BBB complaint, probably not. Privacy.com told that customer federal recordkeeping rules require it to keep identity verification documents and that the California Consumer Privacy Act's deletion right does not apply to that data. The customer disputed both points.
Does Halocard Use Persona?
No. Halocard uses Sumsub for identity verification and names it publicly. Ed has said Halocard is reviewing what Sumsub collects and asking for residual data to be deleted or kept out of training.
Can I Get a Virtual Card Without Identity Verification?
Not from a regulated issuer. Cards that skip KYC tend to be unregulated, frequently declined, and prone to frozen funds. If anonymity is your goal, cash, privacy coins or low-value store-bought gift cards are the realistic options.
Sources
-
Louis Rossmann. Revoking My Endorsement of Privacy.com (YouTube)
-
Privacy Guides. Is Louis Rossmann Right About Privacy.com? (YouTube)
-
Privacy Guides. Is Louis Rossmann Right About Privacy.com? Video Page
-
Privacy Guides Community. Remove Privacy.com
-
Privacy Guides Community. Privacy.com Is Not Private and They're Being Dishonest Calling Themselves That
-
Google Play. Privacy.com App Listing and Reviews
-
Apple App Store. Privacy.com: Virtual Cards Ratings and Reviews
-
Better Business Bureau. Privacy.com Complaints
-
Reddit. Has Anyone Used Privacy.com, r/degoogle
-
Malwarebytes. Age Verification Vendor Persona Left Frontend Exposed, Researchers Say
-
Wikipedia. Persona (Identity Verification Service)
-
Sumsub. Security Incident Update
-
Board of Governors of the Federal Reserve System. 31 CFR 1020.220, Customer Identification Program Requirements for Banks
-
Entrust. Deepfake Attacks Strike Every Five Minutes Amid 244% Surge in Digital Document Forgeries
-
Security.org. 2026 Credit Card Fraud Report
-
Nilson Report via GlobeNewswire. Global Card Fraud Losses at $33 Billion
-
Fenwick. Eighth Circuit Vacates FTC's Click-to-Cancel Rule
-
Trustpilot. Halocard Reviews
Sourced October 1, 2026
*Please see Halocard's Terms of Service or Pricing for the most up to date pricing and fee information. This publication is provided for general information purposes and does not constitute legal, tax or other professional advice from Halocard LLC or its subsidiaries and its affiliates, and it is not intended as a substitute for obtaining advice from a financial advisor or any other professional. We make no representations, warranties or guarantees, whether expressed or implied, that the content in the publication is accurate, complete or up to date.
Halocard Virtual Cards

Instant approval
Create your first card in under 5 minutes.

Private purchases
Purchases never appear on your bank account.

Powered by Visa
Accepted at 175M+ merchants globally.
3 steps to create your virtual credit card
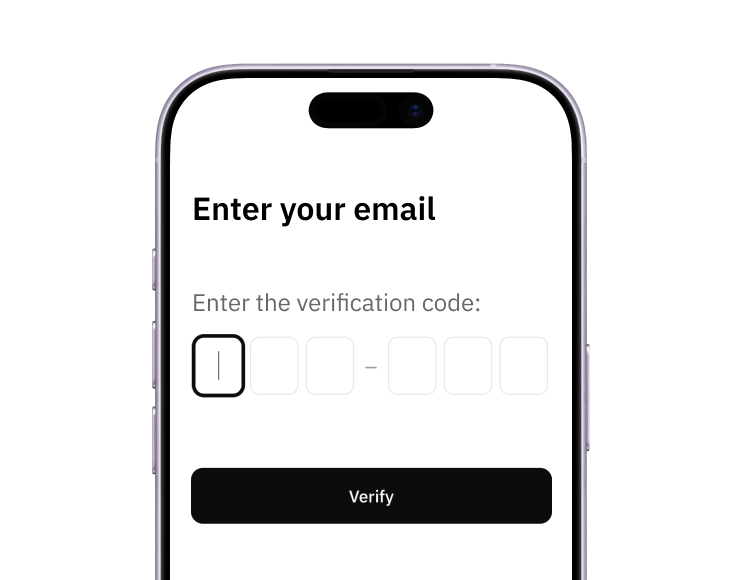
1. Sign up
Create your account from a web browser. No need to download an app.
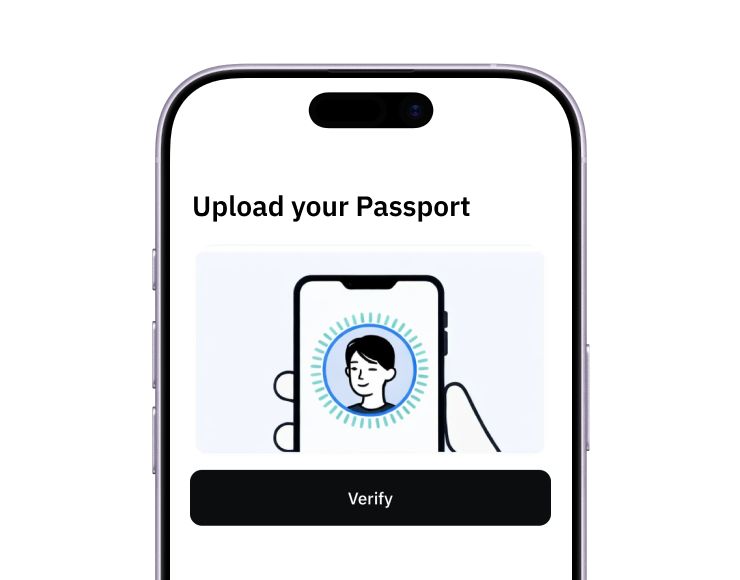
2. Verify
Verify you're a real person in 3 minutes, from the US or any of 120+ countries.
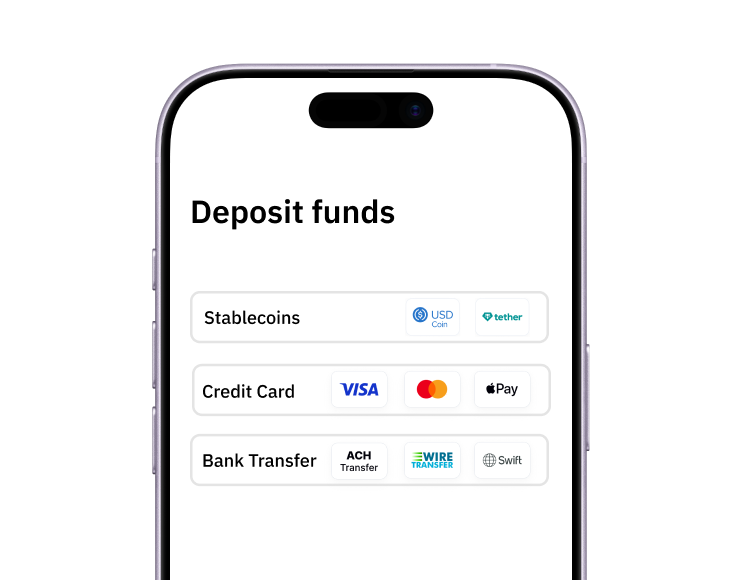
3. Fund
Add funds by debit/credit card, Apple Pay, Google Pay, bank transfer, stablecoins, or crypto.
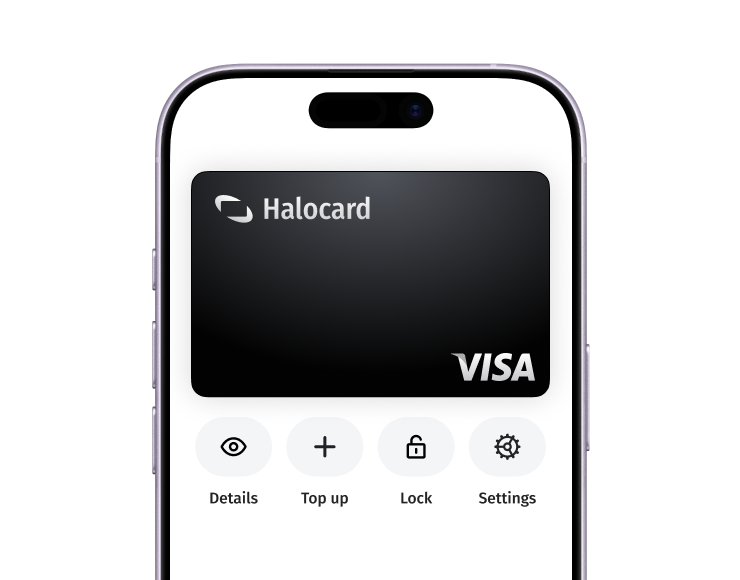
Pay with Halocard
Pay online and in-person wherever Visa is accepted. You can also order a physical Halocard if you prefer.